
Device-Bound USB File Protection for Offline Delivery
Use this workflow to bind a protected package to an approved USB drive or computer instead of handing out ordinary reusable files. Keep source files with the publisher, test the exact recipient environment, and describe restrictions honestly.
Quick answer
Prepare authorized source files in GiliSoft Copy Protect, choose GCP output, set client permissions, select the required USB or computer binding, and test the finished package on the actual recipient device before distribution.
Choose the Right USB Protection Method
| Requirement | Approach | What to verify |
|---|---|---|
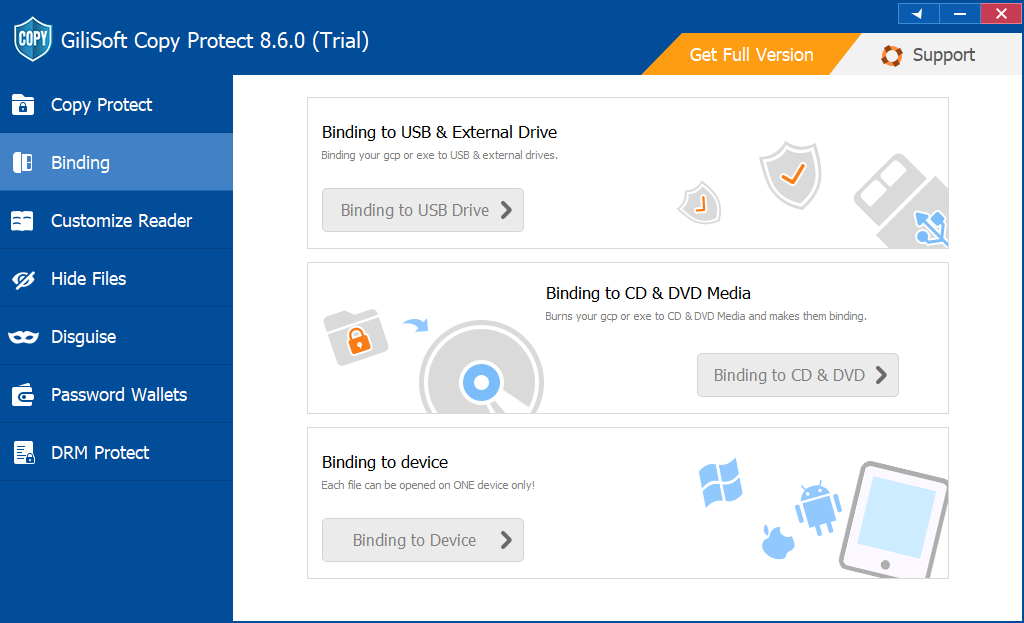
| Bind to USB drive | Use for a known physical delivery medium | Reconnection and replacement procedure |
| Bind to recipient computer | Use when one approved PC is known | Windows compatibility and hardware changes |
| No binding | Use when recipients need supported device flexibility | Client password and use restrictions |
Step-by-Step Protection Workflow
- Define allowed recipient actions
Agree who may open the content, whether printing or copying is allowed, when access ends, and how support or reissue works.
- Prepare a clean source set
Remove drafts, internal notes, hidden material, unnecessary metadata, and editable masters that should not be delivered.
- Create a protected package
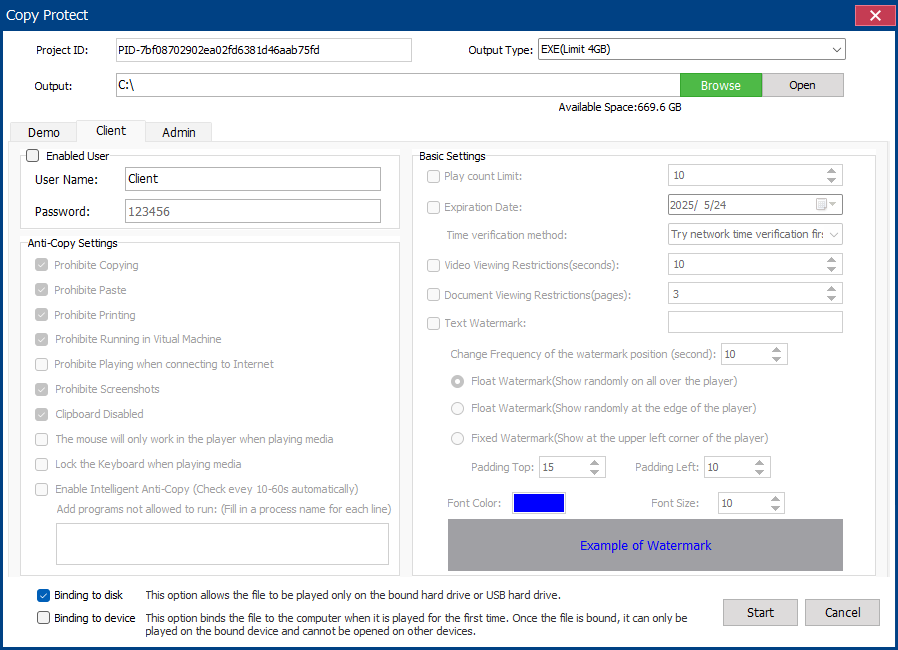
Add files in GiliSoft Copy Protect and choose GCP or EXE output suitable for the content size and recipient environment.
- Configure client settings and optional binding
Create recipient credentials, set copy and print rules, apply watermark or expiry where needed, and bind to USB or a device only when practical.
- Test the recipient experience
Open the finished package on a separate Windows PC with client credentials, reconnect the USB, check every content type, and verify the intended restrictions.
Use the GiliSoft Copy Protect Workspace
These screenshots show the real package, binding, client, or administrator settings. The recipient must be able to open the package in the intended Windows environment.
Verify the USB Delivery Before Handover
| USB identity, reader compatibility, client credentials, and recovery plan | Test with recipient-level credentials, not the publisher's administrator profile. |
|---|---|
| Package integrity | Open every delivered content type, confirm the correct version, and keep the Project ID and admin credentials in publisher records. |
| Support and replacement | Document reader requirements, authorized hardware, expiry, and the procedure for lost, replaced, or failed USB media. |
Frequently Asked Questions
Can GiliSoft Copy Protect protect the files for this USB task?
It can package supported documents, images, video, audio, and mixed folders for controlled viewing. Test the exact source types and the recipient Windows environment before delivery.
Does copy protection stop every possible leak?
No. It reduces ordinary copying, printing, clipboard use, and similar actions under the selected viewer rules, but visible content can still be photographed or recreated.
Is USB binding the same as USB encryption?
No. Binding associates protected output with approved hardware. Removable-drive encryption protects data at rest until the drive is unlocked.
Should recipients get the administrator password?
No. Give them only the client credentials and instructions required to open their package; keep admin credentials and the Project ID with the publisher.
What if the authorized USB drive fails?
Plan a verified reissue procedure before distribution. Do not assume a copied package will open from replacement hardware when binding is enabled.
Should I use GCP or EXE output?
GCP is the standard protected-reader format. EXE can be useful for a self-contained package when the recipient permits executables and the output remains within the product size limit.