
Understand the Encrypted Virtual Disk Lifecycle
| Situation | Recommended approach | Why it fits |
|---|---|---|
| Create | Define location, capacity, and password | Establishes the protected container |
| Open or mount | Unlock the container as a drive | Makes the protected file system available |
| Use | Read, edit, and organize files | Works similarly to an ordinary Windows drive |
| Close or unmount | Remove the open drive view | Returns the container to its protected closed state |
Decide the Container Size, Location, and Purpose
Estimate real capacity
Include current files, expected growth, and enough free space on the host drive.
Choose a reliable host drive
Avoid temporary locations and unstable removable media for the only copy.
Name the purpose
Use a neutral but recognizable locker name for authorized users.
Plan the backup path
Back up the closed container and keep recovery information separate.
Create and Use an Encrypted Virtual Disk: Step by Step
Open the Encrypt Files workspace
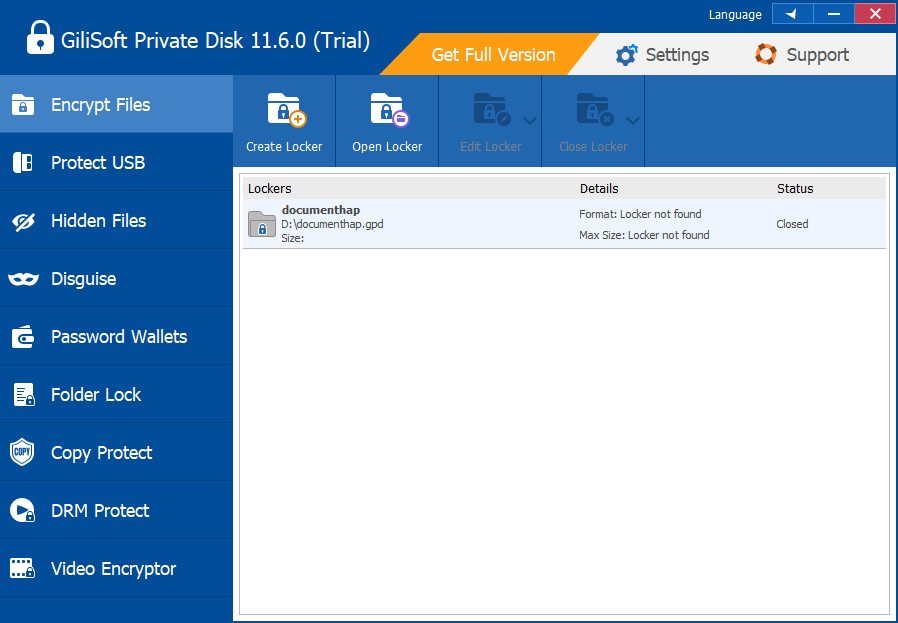
Start GiliSoft Private Disk and select the locker management area.
Create the .gpd container
Choose Create Locker, set the storage path and maximum capacity, and continue.
Protect it with a password
Create a strong unique password and store it through an approved secure method.
Open the virtual disk
Select the locker, choose Open Locker, and enter the password.
Use and organize the files
Copy or create confidential files inside the mounted private drive.
Close and back up the locker
Close dependent applications, close the locker, and back up the complete closed container.

Encrypted Virtual Disk Versus Other Storage Options
Ordinary folder
Convenient, but lacks a dedicated encrypted boundary by itself.
Encrypted virtual disk
Protects a selected workspace that can be mounted when needed.
Full-disk encryption
Protects the broader volume or device when it is offline.
Encrypted removable drive
Protects a physical portable drive and has separate compatibility considerations.
Create Encrypted Virtual Storage with GiliSoft Private Disk
GiliSoft Private Disk turns an encrypted .gpd container into a familiar mounted workspace for Windows files. It is designed for users who want selected confidential data grouped together without encrypting every file individually or relying on folder hiding alone.
Troubleshooting
- The drive has no letter: close and reopen the locker, then review available drive letters.
- Windows says the disk is in use: close files, applications, and Explorer windows before closing it.
- The container is full: review its maximum size and the host drive free space before changing the plan.
- Copying the container fails: close the locker first and copy it as one complete file.
- The password works but files are missing: verify that the correct container was opened and restore only from a known backup.
Security Boundaries to Remember
Protect the Windows session while the private disk is open. Closing the locker limits ordinary drive access, but no single application replaces operating-system updates, malware protection, access control, full-device security, backup, or an organization security policy.
Frequently Asked Questions
What is an encrypted virtual disk?
It is encrypted container storage that appears as a normal drive after it is opened or mounted.
Is it a physical disk?
No. The private drive is backed by a container file stored on a physical drive.
What happens when I close it?
The mounted drive view disappears while the encrypted container remains on its host storage.
Can applications save directly to it?
Yes, while it is open, applications can generally use it like another Windows drive.
Can I move the container?
Close it first, copy the complete container carefully, and verify the destination before removing the original.
How is it different from full-disk encryption?
It protects a selected virtual workspace rather than the entire operating-system or physical data drive.